Next.js Middleware: Building Robust Authentication and Authorization
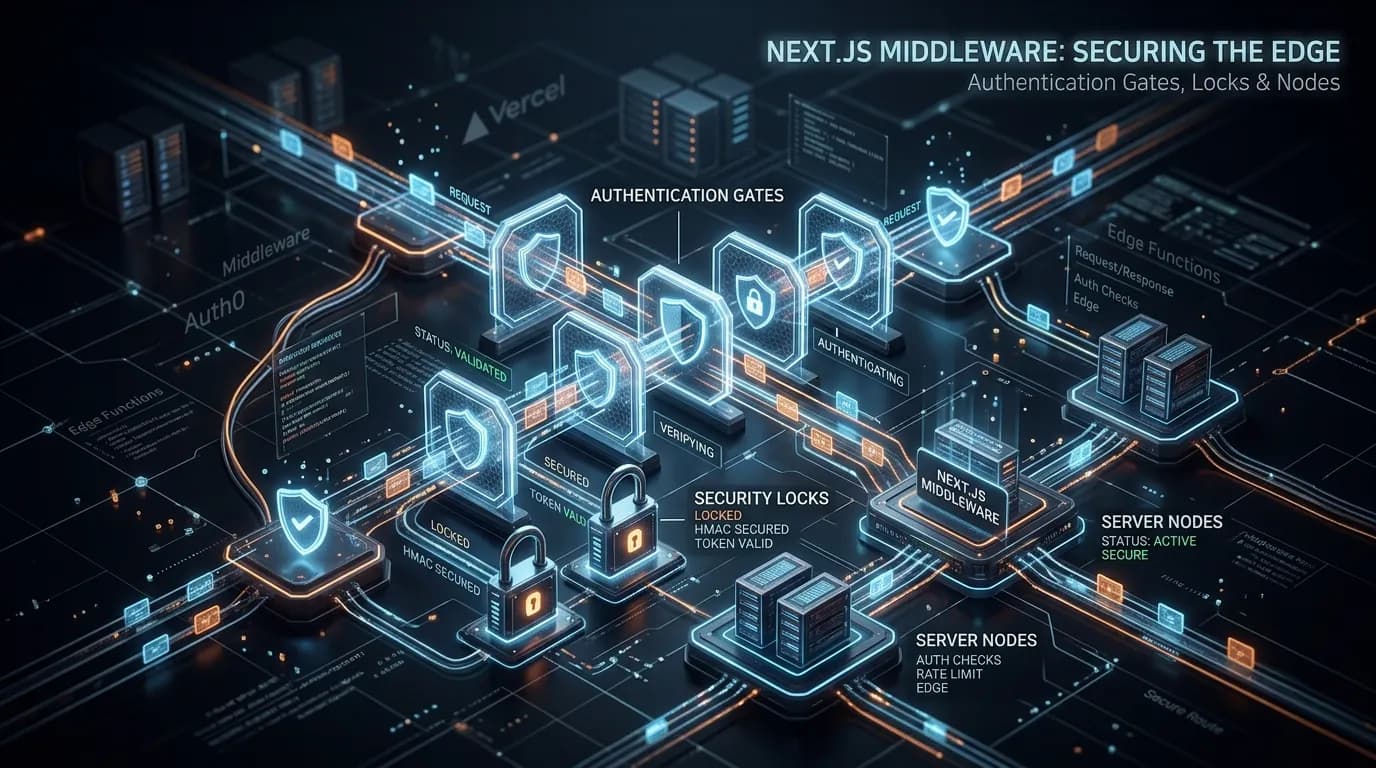

Table of Contents
Authentication and authorization are the bedrock of any secure web application. Historically, in Next.js, securing routes meant wrapping components in Higher-Order Components (HOCs) or performing checks in getServerSideProps on a per-page basis. However, with the maturation of Next.js App Router and Edge Middleware, we now have a vastly superior, centralized, and performant way to handle security.
In 2026, Next.js Middleware runs on the Edge, meaning authentication checks happen incredibly close to the user, before a request even hits your origin server. This article explores how to build robust, scalable authentication and authorization pipelines using Next.js Middleware.
Why Middleware for Authentication?
Middleware allows you to intercept a request, check for a valid session or token, and decide whether to let the request pass, rewrite it, or redirect the user.
Key Benefits:
- Centralization: You no longer need to scatter authentication logic across dozens of pages or layouts. A single
middleware.tsfile can secure your entire application. - Performance: Running on Edge runtimes (like Vercel Edge Functions or Cloudflare Workers) means near-zero cold starts and minimal latency. The check happens before the page even begins rendering.
- Security: By stopping unauthenticated requests at the Edge, you reduce the load on your origin servers and database.
A Basic Authentication Flow
Test and inspect your JWT payload, header claims, and expiry timestamps in real-time with our zero-leak browser decoder:
Let's look at a standard implementation using JSON Web Tokens (JWTs) stored in cookies.
1. Setting up the Middleware
Create a middleware.ts file at the root of your project (or in the src directory if you use one).
import { NextResponse } from 'next/server'
import type { NextRequest } from 'next/server'
import { verifyJwtToken } from '@/lib/auth' // Your custom JWT verifier

export async function middleware(request: NextRequest) {
  const token = request.cookies.get('auth-token')?.value

  const isAuthPage = request.nextUrl.pathname.startsWith('/login') ||
                     request.nextUrl.pathname.startsWith('/register')

  // 1. Check if token exists and is valid
  const verifiedToken = token && (await verifyJwtToken(token).catch((err) => {
    console.error('Failed to verify token', err)
  }))

  // 2. Redirect unauthenticated users away from protected routes
  if (!verifiedToken) {
    if (!isAuthPage && request.nextUrl.pathname.startsWith('/dashboard')) {
      const loginUrl = new URL('/login', request.url)
      loginUrl.searchParams.set('callbackUrl', request.nextUrl.pathname)
      return NextResponse.redirect(loginUrl)
    }
  }

  // 3. Redirect authenticated users away from auth pages
  if (verifiedToken && isAuthPage) {
    return NextResponse.redirect(new URL('/dashboard', request.url))
  }

  // 4. Pass the request through if all checks pass
  return NextResponse.next()
}

// See "Matching Paths" below
export const config = {
  matcher: ['/dashboard/:path*', '/login', '/register'],
}
2. Matching Paths (matcher)
The matcher configuration is crucial. It tells Next.js which routes should trigger the middleware. Running middleware on every single request (including static assets and API routes) is inefficient.
By specifying ['/dashboard/:path*', '/login', '/register'], we ensure our auth logic only runs where it's needed.
Handling Authorization (Role-Based Access Control - RBAC)
Authentication asks "Who are you?". Authorization asks "What are you allowed to do?". Once a user is authenticated, we often need to check their roles or permissions.
We can easily extend our middleware to handle RBAC.
// ... previous imports
import { verifyJwtToken } from '@/lib/auth'

export async function middleware(request: NextRequest) {
  const token = request.cookies.get('auth-token')?.value
  const verifiedToken = token && (await verifyJwtToken(token))

  // ... standard auth checks

  // Handle Authorization
  if (verifiedToken) {
    const userRole = verifiedToken.role // Assuming role is encoded in the JWT

    // Protect admin routes
    if (request.nextUrl.pathname.startsWith('/admin')) {
      if (userRole !== 'ADMIN') {
        // User is authenticated, but not authorized
        return NextResponse.redirect(new URL('/unauthorized', request.url))
      }
    }
  }

  return NextResponse.next()
}

export const config = {
  matcher: ['/dashboard/:path*', '/admin/:path*', '/login'],
}
Security Best Practices in Middleware
- Keep it lightweight: Edge runtimes have size and execution time limits. Do not perform heavy database queries in your middleware. Rely on fast, stateless checks like JWT verification.
- Use
josefor Edge JWTs: Standard Node.jsjsonwebtokenrelies on Node crypto APIs, which are not available on the Edge. Use a library likejosefor signing and verifying tokens in middleware. - Secure Cookies: Ensure your auth cookies are set with
HttpOnly,Secure, andSameSite=laxorstrictto prevent XSS and CSRF attacks. - Graceful Error Handling: If token verification fails (e.g., expired signature), catch the error gracefully and redirect to login, rather than throwing an unhandled exception that causes a 500 error.
Advanced: Passing Data to Server Components
A common challenge is: after verifying the token in middleware, how do we pass the user data to the Server Components without re-verifying the token?
You can mutate the request headers in middleware and read them in your Server Components.
In Middleware:
if (verifiedToken) {
  const requestHeaders = new Headers(request.headers)
  requestHeaders.set('x-user-id', verifiedToken.userId)

  return NextResponse.next({
    request: {
      headers: requestHeaders,
    },
  })
}
In Server Component (page.tsx):
import { headers } from 'next/headers'

export default function DashboardPage() {
  const headersList = headers()
  const userId = headersList.get('x-user-id')

  return <div>Welcome User: {userId}</div>
}
Conclusion
Next.js Middleware provides a powerful, edge-optimized layer for handling authentication and authorization. By centralizing these checks, you drastically simplify your component hierarchy, improve performance, and enhance the overall security posture of your application. When combined with stateless JWTs and careful route matching, it forms the backbone of a modern Next.js architecture.
You Might Also Like
Free In-Browser Developer Tools
Clean AI CLI logs, build cron expressions, decode JWTs, and calculate chmod permissions offline.
Related Articles
TypeScript Alone Isn't Enough: End-to-End Type Safety with Zod in Next.js
TypeScript evaporates at runtime. Learn why static types fail at your API and Server Action boundaries, and how Zod delivers infallible schema validation and inferred typing.
Read more
suppressHydrationWarning in Next.js: Complete Safe Usage & Debugging Guide
Comprehensive guide covering suppresshydrationwarning in next.js: complete safe usage & debugging guide with battle-tested production examples.
Read more
gRPC vs ConnectRPC: Modern Microservices and Browser-Native Protobuf
An architectural evaluation of gRPC vs ConnectRPC in TypeScript and Go. Explore HTTP/1.1 vs HTTP/2 streaming, browser clients without Envoy proxies, and p99 RPC latency.
Read more