Next.js Server Actions
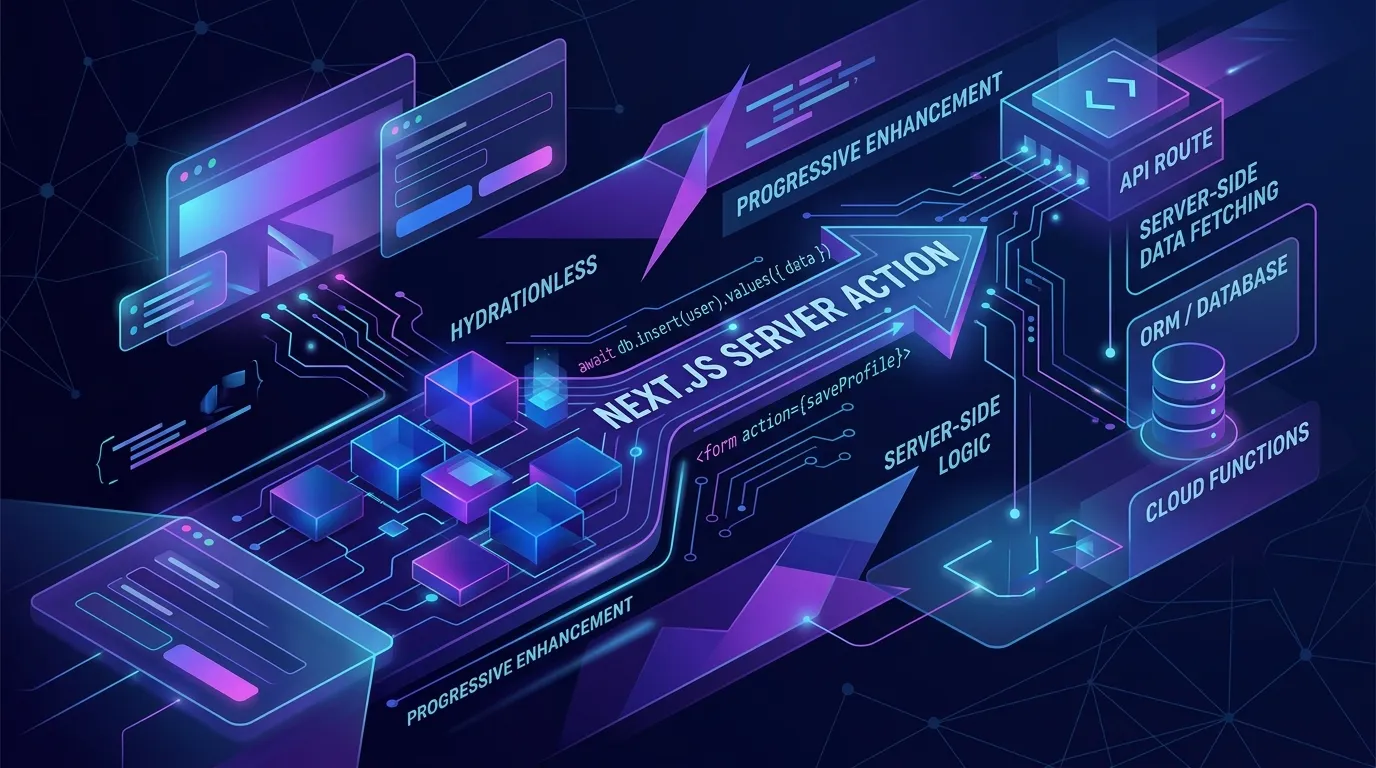

Table of Contents
When React first revolutionized the frontend ecosystem, the separation of client-side logic and server-side data fetching was a strict boundary. Over the years, Next.js steadily bridged this gap—first with getServerSideProps and getStaticProps, then with the App Router and Server Components. But what about mutations? How do we seamlessly send data from the client back to the server without the friction of building bespoke API endpoints?
Enter Server Actions. Introduced as an alpha feature in Next.js 13 and stabilized in Next.js 14, Server Actions fundamentally rewrite the rules of full-stack data mutation in React applications. In this deep dive, we will unpack the mechanics of Server Actions, their security implications, and how they interact with caching, progressive enhancement, and React's evolving primitive hooks.
The Problem With Traditional Mutations
Before Server Actions, a typical form submission in a React application required an orchestra of interconnected parts:
- Client-side State Management: Controlled inputs using
useStateor complex form libraries likereact-hook-form. - API Routes: A dedicated backend endpoint (e.g.,
/api/submit) to receive and process the payload. - Fetching Logic: Using
fetchor a data-fetching library (like React Query or SWR) to transmit the payload, handle loading states, and parse the response. - Error Handling: Synchronizing server-side validation errors back to the client-side state.
- Revalidation: Manually triggering a refetch to ensure the UI reflects the mutated data.
While functional, this approach introduced significant boilerplate and network waterfalls. It also forced developers into tight coupling between frontend components and backend API routes.
How Server Actions Work Under the Hood
A Server Action is, at its core, an asynchronous function defined on the server that can be called directly from client or server components. When you define a function with the "use server" directive, Next.js performs a compilation step that fundamentally transforms how that function is exposed.
// actions.ts
"use server";

import { db } from "@/lib/db";
import { revalidatePath } from "next/cache";

export async function createPost(formData: FormData) {
  const title = formData.get("title");

  await db.post.create({
    data: { title: title as string }
  });

  revalidatePath("/posts");
}
When you import and invoke this function from a Client Component, Next.js does not bundle the function's code into the client bundle. Instead, the bundler creates a remote procedure call (RPC) mechanism. The client bundle receives a proxy function. When this proxy is executed, it sends an HTTP POST request to the Next.js server containing the action's identifier and its arguments.
The server decodes the payload, executes the original function securely, and returns the result (along with any UI updates or revalidation instructions). This entire process bypasses the need for an explicit API route, drastically reducing boilerplate and cognitive load.
Deep Integration with the Next.js Cache
One of the most powerful aspects of Server Actions is their deep integration with the Next.js App Router cache. In traditional REST or GraphQL mutations, updating data on the server means you must manually invalidate client-side caches (e.g., using React Query's invalidateQueries).
With Server Actions, cache invalidation is built into the framework via revalidatePath and revalidateTag. When an action completes, Next.js can respond with an instruction to the client router to refetch specific paths. This happens in a single network round-trip.
For example:
export async function updateProfile(data: UserData) {
  "use server"
  await updateDb(data);
  revalidateTag("user-profile");
}
Upon execution, Next.js will automatically purge the server-side cache for the user-profile tag and instruct the client router to apply the updated Server Component payload seamlessly, preserving client-side state where possible.
Security Considerations: The Invisible API
A common misconception is that Server Actions are "magic" and therefore insecure. In reality, Server Actions are functionally identical to public API endpoints. When you expose a Server Action, it can be invoked by anyone who can make an HTTP request to your domain.
Because of this, you must treat every Server Action as an untrusted entry point:
- Authentication and Authorization: You must explicitly check the user's session and permissions inside every action.
- Input Validation: Never trust the
FormDataor arguments passed to a Server Action. Always use a schema validation library like Zod to sanitize and validate inputs before interacting with your database. - Cross-Site Request Forgery (CSRF): Next.js automatically implements CSRF protection for Server Actions by enforcing strict origin checks and utilizing specific headers, mitigating one of the most common web vulnerabilities.
export async function secureAction(data: unknown) {
  "use server";

  const session = await getSession();
  if (!session) throw new Error("Unauthorized");

  const parsed = mySchema.safeParse(data);
  if (!parsed.success) throw new Error("Invalid input");

  // Safe to proceed
}
Progressive Enhancement and Form Submissions
Server Actions shine brightest when used natively with HTML forms. By passing a Server Action directly to the action attribute of a <form> element, you get progressive enhancement out of the box.
import { createPost } from "./actions";

export default function PostForm() {
  return (
    <form action={createPost}>
      <input type="text" name="title" required />
      <button type="submit">Create</button>
    </form>
  );
}
If JavaScript is disabled or fails to load, the browser will fall back to a standard URL-encoded form submission. Next.js handles this seamlessly, executing the action and redirecting the user back to the rendered page. When JavaScript is enabled, React intercepts the submission, prevents the full-page reload, and handles the request via fetch, allowing for smooth, SPA-like transitions.
React 19 introduces hooks like useActionState and useFormStatus to handle pending states and optimistic UI updates natively. This further reduces the reliance on external state management libraries, pulling mutation logic back to the platform.
The Future of React Architecture
Next.js Server Actions represent a fundamental shift in how we architect full-stack React applications. By collapsing the distance between the client and the server, reducing the need for explicit API routes, and integrating deeply with caching mechanisms, Server Actions provide a developer experience that feels incredibly modern yet grounded in fundamental web standards.
While they require a disciplined approach to security and validation, the trade-off in productivity and simplicity is undeniable. As the React ecosystem continues to evolve, the RPC-style mutation pattern pioneered by Server Actions is poised to become the standard for data mutation across the framework.
You Might Also Like
Free In-Browser Developer Tools
Clean AI CLI logs, build cron expressions, decode JWTs, and calculate chmod permissions offline.
Related Articles
suppressHydrationWarning in Next.js: Complete Safe Usage & Debugging Guide
Comprehensive guide covering suppresshydrationwarning in next.js: complete safe usage & debugging guide with battle-tested production examples.
Read more
Next.js 15 Server Actions vs Route Handlers: Deep Architectural Comparison
Master when to choose Server Actions versus Route Handlers in Next.js 15. Deep dive into progressive enhancement, caching behavior, RPC protocols, and security boundaries.
Read more
State Management in React 2026: Beyond Redux
Comprehensive guide to React state management in 2026: comparing React 19 actions, TanStack Query server state, Zustand, Jotai, and Signals.
Read more