Memory Safety in Zig
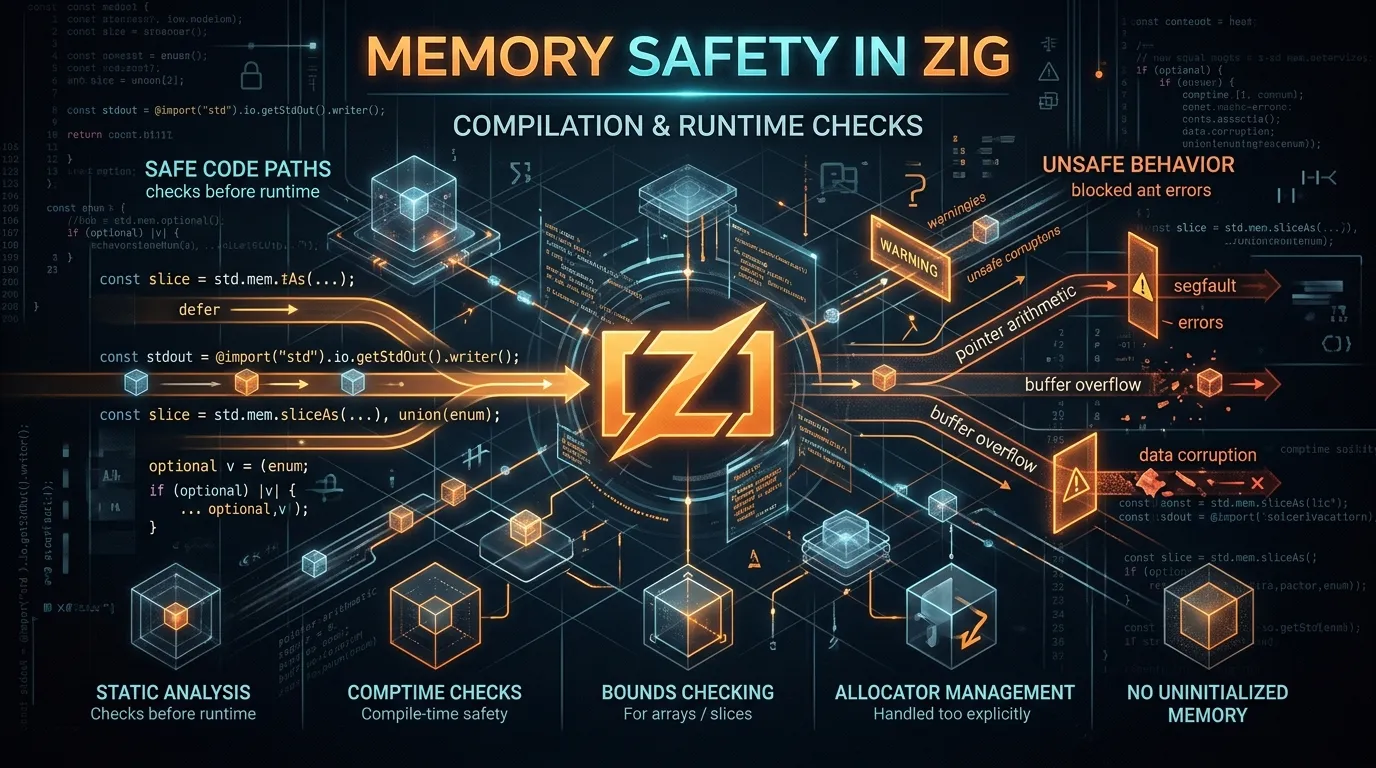

Table of Contents
When developers discuss memory safety in modern systems programming, the conversation almost invariably turns to Rust and its renowned borrow checker. Rust provides compile-time guarantees that eliminate entire classes of memory errors, such as use-after-free and double-free vulnerabilities. However, Zig—a relatively new, yet rapidly maturing systems programming language—takes a fundamentally different approach to achieving memory safety. Rather than relying on a complex type system and strict compile-time aliasing rules, Zig emphasizes explicit allocation, runtime instrumentation, and developer control. This post explores the technical nuances of memory safety in Zig, contrasting it with other systems languages and examining how it achieves robust safety guarantees through a combination of language features and tooling.
The Philosophy of Explicit Memory Management
Zig's core philosophy is that there is no hidden control flow and no hidden memory allocation. Unlike C or C++, where standard library functions often allocate memory implicitly using malloc under the hood, Zig requires the programmer to pass an allocator explicitly to any function that needs to allocate memory.
const std = @import("std");

pub fn main() !void {
    // We explicitly create an allocator
    var gpa = std.heap.GeneralPurposeAllocator(.{}){};
    defer _ = gpa.deinit();
    const allocator = gpa.allocator();

    // The allocator is passed as an argument
    var list = std.ArrayList(i32).init(allocator);
    defer list.deinit();

    try list.append(42);
}
This explicitness forces developers to think about the lifecycle of every allocated object and makes it trivially easy to swap out allocators for different use cases. In the context of memory safety, this means that memory usage is localized and transparent, reducing the likelihood of leaks or mismanagement caused by obscure library behavior.
Spatial Memory Safety: Bounds Checking and Pointers
Spatial memory safety refers to ensuring that a program does not access memory outside the bounds of an allocated object. In C, array bounds checking is virtually nonexistent, leading to the infamous buffer overflow vulnerabilities. Zig addresses this through robust bounds checking and a more nuanced pointer system.
In Zig, arrays and slices inherently know their length. When you access an element of a slice, Zig performs a bounds check. In Debug and ReleaseSafe build modes, accessing an out-of-bounds index will result in a deterministically handled panic, rather than undefined behavior (UB).
const array = [_]i32{ 1, 2, 3 };
// This will panic at runtime in Safe modes:
// const out_of_bounds = array[5];
Furthermore, Zig distinguishes between single-item pointers (*T), many-item pointers ([*]T), and slices ([]T). A single-item pointer cannot be used for pointer arithmetic. If you need to iterate over memory, you must use a slice, which carries the length information and allows for bounds-checked operations. This design choice severely restricts the potential for erroneous pointer arithmetic, which is a major source of spatial memory violations in C and C++.
Temporal Memory Safety: The GeneralPurposeAllocator
Temporal memory safety ensures that memory is not accessed after it has been freed (use-after-free) and that memory is not freed multiple times (double-free). Rust solves this at compile time by tracking lifetimes. Zig relies on runtime instrumentation, primarily through its GeneralPurposeAllocator (GPA).
The GPA in Zig is not just a mechanism for requesting memory from the OS; it is a powerful debugging tool. When running in Debug mode, the GPA tracks all allocations and deallocations. It can detect memory leaks upon deinitialization and, crucially, it can detect use-after-free errors.
When memory is freed, the GPA can poison that memory region. If a dangling pointer is later dereferenced, the poisoned memory will trigger a hard crash or a detectable failure, rather than silently corrupting data or allowing arbitrary code execution. This "fail-fast" behavior is critical for identifying memory bugs during the development cycle.
test "use after free detection" {
    var gpa = std.heap.GeneralPurposeAllocator(.{}){};
    defer std.testing.expect(gpa.deinit() == .ok) catch @panic("leak");
    const allocator = gpa.allocator();

    const ptr = try allocator.create(i32);
    ptr.* = 100;

    // Free the memory
    allocator.destroy(ptr);

    // This use-after-free will trigger a crash in Debug mode
    // ptr.* = 200;
}
The Role of defer and errdefer
Resource management in Zig is heavily reliant on the defer and errdefer statements. These constructs ensure that cleanup code is executed regardless of how a block of code exits, similar to RAII in C++ but without the implicit destruction semantics.
The defer statement schedules a piece of code to run at the end of the current scope. This is typically used for freeing memory or releasing resources (e.g., closing file handles).
The errdefer statement is even more powerful for error handling. It schedules cleanup code to run only if the current block exits with an error. This is invaluable when constructing complex objects that require multiple allocations. If a later allocation fails, errdefer can cleanly tear down the partially constructed object, preventing memory leaks in error paths.
pub fn createComplexObject(allocator: std.mem.Allocator) !*ComplexObject {
    const obj = try allocator.create(ComplexObject);
    errdefer allocator.destroy(obj);

    obj.buffer1 = try allocator.alloc(u8, 1024);
    errdefer allocator.free(obj.buffer1);

    // If this fails, buffer1 and obj will be cleanly freed
    obj.buffer2 = try allocator.alloc(u8, 2048);

    return obj;
}
This structured approach to resource management significantly reduces the cognitive load on the developer and minimizes the risk of temporal memory errors caused by convoluted error-handling logic.
Trade-offs and the Road Ahead
Zig's approach to memory safety relies heavily on the developer's discipline to use defer correctly and to thoroughly test code in Debug or ReleaseSafe modes. It does not provide the airtight, mathematically provable guarantees that Rust's borrow checker offers. A determined or careless developer can still write a use-after-free bug in Zig that might slip into a ReleaseFast build (where safety checks are disabled for performance).
However, this trade-off comes with distinct advantages. Zig's learning curve is arguably shallower than Rust's, as developers do not have to wrestle with a borrow checker. Data structures that are notoriously difficult to implement in safe Rust (like doubly linked lists or graphs) are straightforward to implement in Zig.
Furthermore, Zig's explicit allocators open the door to advanced memory management techniques. Arena allocators, for instance, can allocate a vast amount of memory for a specific task and free it all at once by discarding the arena, entirely bypassing the need for individual destroy or free calls. This eliminates temporal memory errors within the context of the arena, as individual objects are never explicitly freed.
In conclusion, Zig offers a pragmatic and highly effective approach to memory safety. By combining explicit allocation, powerful runtime checking in debug builds, robust spatial safety through slices, and clean resource management via defer, Zig empowers developers to write safe, high-performance systems code without sacrificing control or dealing with steep compile-time constraints. It represents a fascinating alternative in the ongoing evolution of systems programming languages.
You Might Also Like
Free In-Browser Developer Tools
Clean AI CLI logs, build cron expressions, decode JWTs, and calculate chmod permissions offline.
Related Articles
Quantum Computing for Developers
A developer guide to quantum computing: write quantum algorithms with Qiskit, understand quantum gates, and simulate circuits on classical hardware.
Read more
Distributed Tracing with OpenTelemetry
Instrument microservices with OpenTelemetry distributed tracing: trace cross-service context propagation, latency bottlenecks, and export to Jaeger.
Read more
WebGL and Three.js Performance
Optimize 3D web performance with WebGL and Three.js: master draw call batching, shader profiling, geometry instancing, and GPU memory management.
Read more